시험대비NSE6_FMG_AD-7.6최신업데이트인증공부자료공부자료
Itexamdump 에서Fortinet NSE6_FMG_AD-7.6 덤프를 구매하시면 일년무료 업데이트서비스를 받을수 있습니다.일년무료 업데이트서비스란 구매일로부터 1년동안 구매한 덤프가 업데이트될때마다 구매시 사용한 메일주소로 가장 최신버전을 보내드리는것을 의미합니다. Fortinet NSE6_FMG_AD-7.6덤프에는 가장 최신시험문제의 기출문제가 포함되어있어 높은 적주율을 자랑하고 있습니다.
Fortinet NSE6_FMG_AD-7.6 Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Troubleshooting | - Troubleshooting scenarios
|
| Administration | - FortiManager features
|
| Advanced Configuration | - Advanced deployment
|
| Device Manager | - Device management
|
| Policy and Objects | - Policy management
|
>> NSE6_FMG_AD-7.6최신 업데이트 인증공부자료 <<
100% 합격보장 가능한 NSE6_FMG_AD-7.6최신 업데이트 인증공부자료 시험자료
Itexamdump이 바로 아주 좋은Fortinet NSE6_FMG_AD-7.6인증시험덤프를 제공할 수 있는 사이트입니다. Itexamdump 의 덤프자료는 IT관련지식이 없는 혹은 적은 분들이 고난의도인Fortinet NSE6_FMG_AD-7.6인증시험을 패스할 수 있습니다. 만약Itexamdump에서 제공하는Fortinet NSE6_FMG_AD-7.6인증시험덤프를 장바구니에 넣는다면 여러분은 많은 시간과 정신력을 절약하실 수 있습니다. 우리Itexamdump 의Fortinet NSE6_FMG_AD-7.6인증시험덤프는 Itexamdump전문적으로Fortinet NSE6_FMG_AD-7.6인증시험대비로 만들어진 최고의 자료입니다.
최신 NSE 6 Network Security Specialist NSE6_FMG_AD-7.6 무료샘플문제 (Q58-Q63):
질문 # 58
Refer to the exhibit.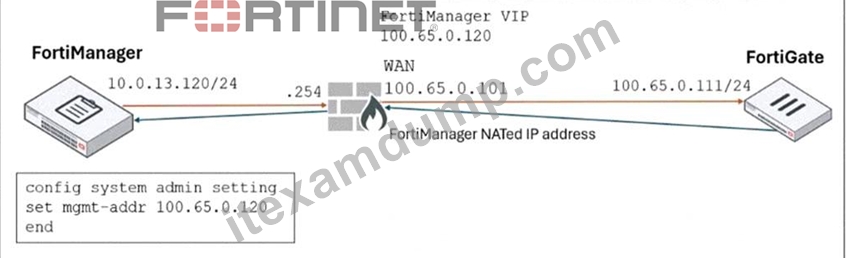
FortiManager
is operating behind a network address translation (NAT) device, and the
administrator configured the FortiManager NATed IP address under the
FortiManager system administration settings.
What is the expected result
during discovery?
- A. FortiManager sets both the 100.65.0.120 IP address and 10.0.13.120 IP address on FortiGate.
- B. FortiManager sets the 100.65.0.120 IP address on FortiGate.
- C. FortiManager sets both the 100.65.0.120 IP address and 100.65.0.101 IP address on FortiGate.
- D. FortiManager sets the 100.65.0.101 IP address on FortiGate.
정답:B
설명:
When FortiManager is behind a NAT device, setting the NATed IP address
(100.65.0.120) in the system admin settings causes FortiManager to use that
NATed IP address for communication and configuration with FortiGate during
discovery and management operations.
질문 # 59
What can you conclude from the failed
installation log shown in the exhibit?
- A. Policy ID 2 is installed without the remote user student.
- B. Policy ID 2 is installed without a source address.
- C. Policy ID 2 will not be installed.
- D. Policy ID 2 is installed in the disabled state.
정답:A
설명:
The correct answer is D. The lab guide explains that when an
installation fails, the installation log shows the commands that the managed
device received and accepted, as well as the commands that the managed device
did not accept.
From the exhibit, FortiGate accepted the policy creation
commands for policy ID 2 such as set srcintf port3, set dstintf port1, set
srcaddr all, set dstaddr all, set action accept, and set schedule always.
However, the line set users student failed with "entry not found in datasource"
and "value parse error before ' student ' ". That shows the user reference was
not accepted, while the rest of the policy commands were processed. Therefore,
policy ID 2 is still created, but without the remote user student. This rules
out A, B, and C.
=========
질문 # 60
An administrator upgrades FortiManager with
workspace mode per ADOM enabled to the latest version but notices that the ADOM
versions did not change.
Why were the ADOMs not upgraded?
- A. FortiManager does not automatically upgrade ADOMs after a firmware upgrade.
- B. A FortiManager process task is stuck and blocking the ADOM upgrade, so the administrator must fix it.
- C. A user had all ADOMs locked before the upgrade, which stopped them from being upgraded.
- D. The administrator did not run the database integrity check before performing the upgrade.
정답:A
설명:
The correct answer is B. The FortiManager 7.6 Administrator Study
Guide gives the exact extract: "Also note when you upgrade the FortiManager
firmware version the existing ADOMs are not automatically upgraded." This
directly explains why the administrator saw the FortiManager upgrade complete
while the ADOM versions remained unchanged.
The same section also explains
that ADOM upgrades are a separate action: "You can upgrade an ADOM in System
Settings > ADOMs" and "Can upgrade to one version higher at a time." In
addition, the guide recommends: "upgrade all devices first, and then upgrade the
ADOM." So the issue is not workspace mode, locked ADOMs, or a stuck task. The
ADOMs simply require their own manual upgrade step after the FortiManager
firmware upgrade.
질문 # 61
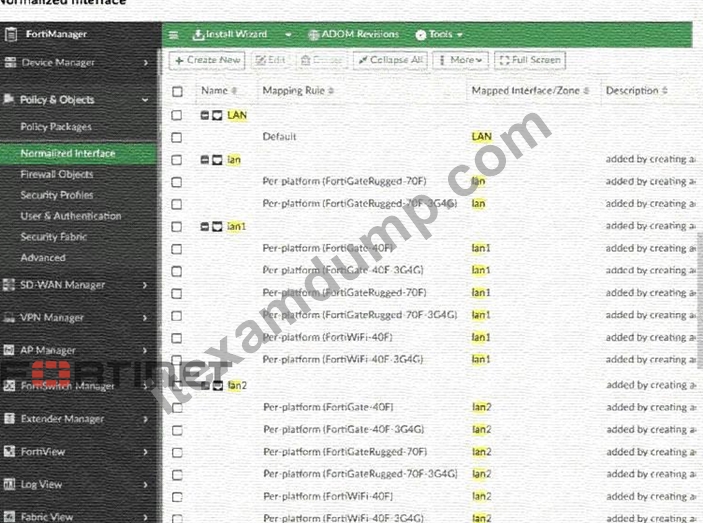
Refer to the exhibits.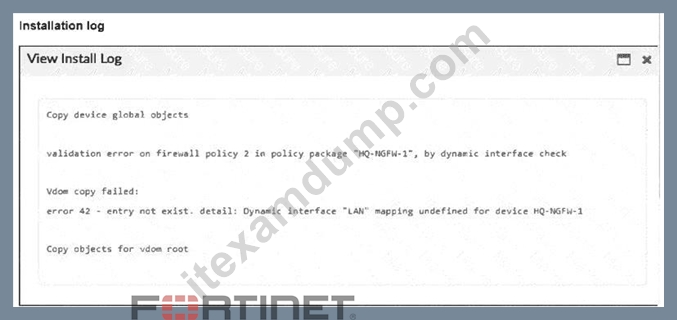
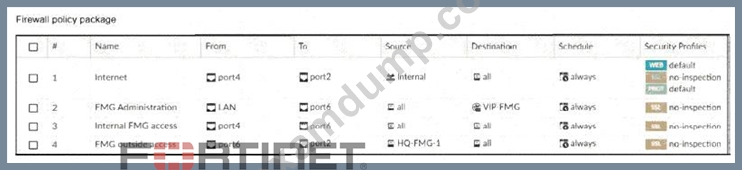
An
administrator must replace the source LAN interface in policy ID 2 on their
FortiGateRugged-70F.
However, when they try to install the policy package,
they receive the error shown in the exhibit.
What should the administrator do
to resolve the error?
- A. Use a metadata variable to dynamically assign an interface when this error occurs.
- B. Use the API to assign a system template interface for FortiGateRugged-70F model.
- C. Replace LAN with lan1, which is supported by FortiGateRugged-70F models.
- D. Create a per-device mapping for the LAN interface.
정답:D
설명:
The correct answer is C. The installation log explicitly says:
"Dynamic interface 'LAN' mapping undefined for device HQ-NGFW-1". That means the
policy is using a normalized interface, but FortiManager has no valid mapping
for that device. The FortiManager 7.6 Administrator Study Guide states that
"Interfaces are mapped per device, per platform, or both" and "When the
normalized interface is used in a policy, the per- device mappings have higher
priority than per-platform mappings." The lab guide also shows that during
import or policy mapping fixes, the administrator can set the Mapping Type to
Per-Device for interfaces.
So the correct fix is to create a per-device
mapping for the normalized interface LAN for that FortiGateRugged-70F.
Hardcoding lan1 in the policy is not the best FortiManager method because
interface mapping is designed specifically to avoid that.
=========
질문 # 62
An administrator receives the import report
after importing policies into the policy package layer.
Based
on the import report, how did FortiManager handle the profile-protocol-options
object named default?
- A. FortiManager created a new service category in its database.
- B. FortiManager deleted the duplicate value from its database.
- C. FortiManager updated the duplicate value in the FortiGate database.
- D. FortiManager did not update its database with the value.
정답:D
설명:
The import report clearly shows: " firewall profile-protocol-options "
, SKIPPED, " (name=default, oid=3491, DUPLICATE) " . In FortiManager import
reporting, SKIPPED means the object was not imported or updated, and DUPLICATE
means an object with that identity already exists in the ADOM database. So
FortiManager did not update its database with the imported value for the object
default, which makes C correct.
The lab guide reinforces this behavior in the
conflict-handling workflow. It explains that during import, FortiManager checks
for duplicate names and conflicts, and for conflicting objects the administrator
may need to choose whether to keep the value from FortiGate or FortiManager. For
the default Firewall Profile-Protocol- Options object, the guide specifically
discusses keeping the existing FortiManager value to avoid unnecessary
changes.
=========
질문 # 63
......
우리Itexamdump에서는 각종IT시험에 관심있는분들을 위하여, 여러 가지 인증시험자료를 제공하는 사이트입니다. 우리Itexamdump는 많은 분들이 IT인증시험을 응시하여 성공할수록 도와주는 사이트입니다. 우리의 파워는 아주 대단하답니다. 여러분은 우리Itexamdump 사이트에서 제공하는Fortinet NSE6_FMG_AD-7.6관련자료의 일부분문제와답등 샘플을 무료로 다운받아 체험해봄으로 우리에 믿음이 생기게 될 것입니다.
NSE6_FMG_AD-7.6퍼펙트 인증공부: https://www.itexamdump.com/NSE6_FMG_AD-7.6.html
- NSE6_FMG_AD-7.6최신 인증시험 기출자료 🕧 NSE6_FMG_AD-7.6덤프문제집 😲 NSE6_FMG_AD-7.6최신기출자료 ✒ 지금☀ www.pass4test.net ️☀️을(를) 열고 무료 다운로드를 위해⏩ NSE6_FMG_AD-7.6 ⏪를 검색하십시오NSE6_FMG_AD-7.6시험기출문제
- NSE6_FMG_AD-7.6최신 업데이트 인증공부자료 완벽한 시험대비 덤프공부 🐝 { www.itdumpskr.com }을(를) 열고➠ NSE6_FMG_AD-7.6 🠰를 입력하고 무료 다운로드를 받으십시오NSE6_FMG_AD-7.6시험내용
- 최신 NSE6_FMG_AD-7.6최신 업데이트 인증공부자료 인증시험대비 공부문제 🍛 ▶ www.pass4test.net ◀에서⮆ NSE6_FMG_AD-7.6 ⮄를 검색하고 무료 다운로드 받기NSE6_FMG_AD-7.6인기자격증 덤프문제
- NSE6_FMG_AD-7.6완벽한 인증자료 🐾 NSE6_FMG_AD-7.6최신기출자료 🚣 NSE6_FMG_AD-7.6완벽한 인증자료 🐤 [ www.itdumpskr.com ]의 무료 다운로드▷ NSE6_FMG_AD-7.6 ◁페이지가 지금 열립니다NSE6_FMG_AD-7.6퍼펙트 덤프데모 다운로드
- NSE6_FMG_AD-7.6최고품질 덤프자료 💟 NSE6_FMG_AD-7.6완벽한 인증시험덤프 🖖 NSE6_FMG_AD-7.6완벽한 인증시험덤프 😘 “ www.dumptop.com ”에서{ NSE6_FMG_AD-7.6 }를 검색하고 무료로 다운로드하세요NSE6_FMG_AD-7.6최신버전 덤프공부
- NSE6_FMG_AD-7.6덤프최신버전 🔪 NSE6_FMG_AD-7.6최고품질 덤프자료 🕖 NSE6_FMG_AD-7.6최신버전 덤프공부 🏴 ( www.itdumpskr.com )에서⇛ NSE6_FMG_AD-7.6 ⇚를 검색하고 무료 다운로드 받기NSE6_FMG_AD-7.6덤프문제집
- NSE6_FMG_AD-7.6인기시험덤프 🥢 NSE6_FMG_AD-7.6완벽한 덤프자료 😦 NSE6_FMG_AD-7.6최신기출자료 🎭 ⇛ www.dumptop.com ⇚을(를) 열고➡ NSE6_FMG_AD-7.6 ️⬅️를 검색하여 시험 자료를 무료로 다운로드하십시오NSE6_FMG_AD-7.6최신기출자료
- 시험준비에 가장 좋은 NSE6_FMG_AD-7.6최신 업데이트 인증공부자료 최신버전 덤프데모 문제 다운 🙊 무료로 쉽게 다운로드하려면[ www.itdumpskr.com ]에서[ NSE6_FMG_AD-7.6 ]를 검색하세요NSE6_FMG_AD-7.6시험대비
- 높은 통과율 NSE6_FMG_AD-7.6최신 업데이트 인증공부자료 시험덤프로 시험패스가능 ❇ 【 www.dumptop.com 】을(를) 열고✔ NSE6_FMG_AD-7.6 ️✔️를 검색하여 시험 자료를 무료로 다운로드하십시오NSE6_FMG_AD-7.6덤프문제집
- NSE6_FMG_AD-7.6최신 업데이트 인증공부자료 100%시험패스 가능한 덤프문제 🧍 “ www.itdumpskr.com ”에서 검색만 하면✔ NSE6_FMG_AD-7.6 ️✔️를 무료로 다운로드할 수 있습니다NSE6_FMG_AD-7.6최신버전 덤프공부
- NSE6_FMG_AD-7.6최신기출자료 🕒 NSE6_FMG_AD-7.6최고품질 덤프자료 🙌 NSE6_FMG_AD-7.6최신버전 덤프공부 🔜 “ www.dumptop.com ”의 무료 다운로드{ NSE6_FMG_AD-7.6 }페이지가 지금 열립니다NSE6_FMG_AD-7.6적중율 높은 시험덤프공부
- myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, Disposable vapes


Comments
Post a Comment